Terraform, Pulumi, and CloudFormation – Comparing the Top Infrastructure as Code Tools So Far

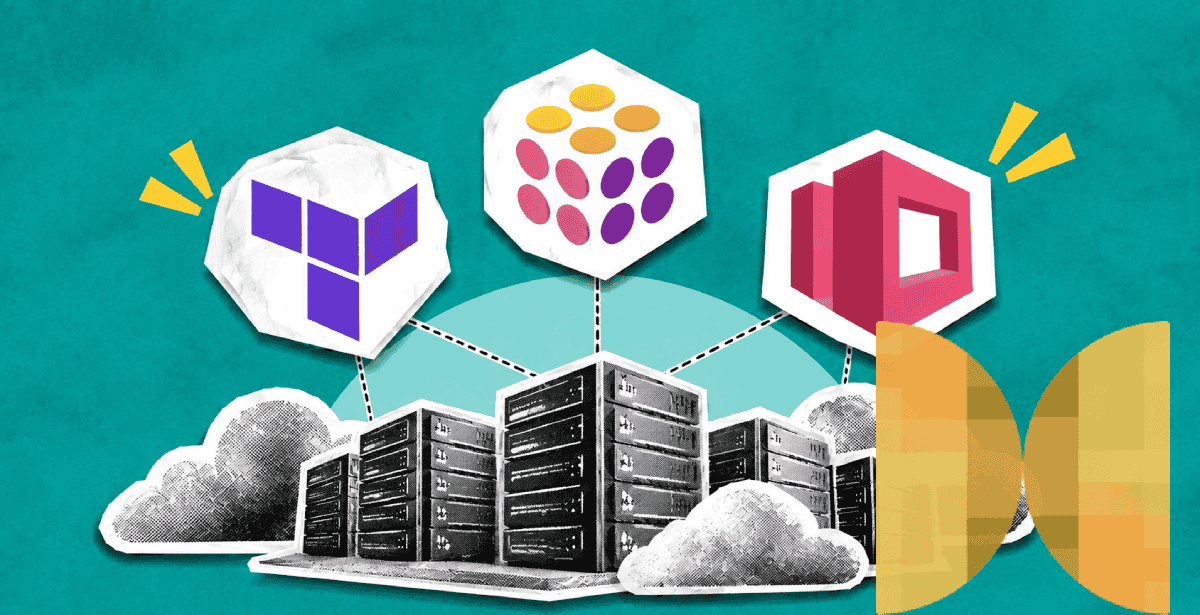
Every cloud team eventually asks the same question. Should infrastructure live in a config file or in real code?
Infrastructure as code tools answer that question differently depending on which one a team picks. Terraform, Pulumi, and CloudFormation each take a genuinely distinct approach to provisioning.
Terraform IaC: The Declarative Default Most Teams Start With
Terraform is the king of infrastructure as code tools. It has a 76% market share among organizations using IaC tools, and is mainly adopted by enterprises globally.
What Is Terraform?
Terraform IaC is an open-source tool that turns written configuration into real cloud resources through a plan-and-apply workflow.
The workflow itself is simple to describe at a high level. Write configuration, run a plan to preview changes, then apply that plan to provision real infrastructure.
That preview step is what makes Terraform genuinely safer than manual provisioning through a cloud console. Nobody applies a change blind, without first seeing exactly what will happen.
Modules extend that simplicity further, letting teams package reusable infrastructure patterns once and reuse them everywhere. A well-built module library becomes a genuine productivity multiplier over time.
Why Terraform is a Great Option
Terraform remains one of the leading infrastructure as code tools because of its declarative approach, extensive provider ecosystem, and active community.
Key strengths and considerations include:
- Declarative Configuration – Uses HashiCorp Configuration Language (HCL) to define the desired infrastructure state rather than step-by-step instructions. Its readable plan output helps engineers review changes before applying them.
- Broad Provider Support – Supports AWS, Azure, GCP, and hundreds of other services through a consistent provider interface, reducing the need for separate tools.
- State Management – Requires careful handling of state files to prevent provisioning errors. Remote state storage with locking is essential when multiple engineers manage the same infrastructure.
- Mature Ecosystem – Community modules save engineering time by providing reusable solutions for common provisioning patterns. However, teams should review third-party modules for security and quality before adoption.
- Version Control – Pinning module versions prevents unexpected upstream changes from breaking production deployments. Automatically tracking the latest releases can introduce unreviewed risks.
According to The State of IaC 2025, 89% of surveyed organizations have adopted IaC, although only 6% report complete coverage. Terraform remains the majority choice, despite gradually losing market dominance.
Its established ecosystem, extensive documentation, and active community continue to make it a practical choice for managing infrastructure at scale.
How DPL Used Terraform to Automate Cloud CRM Infrastructure for a Government Agency
Sindh Ombudsman needed cloud infrastructure that could scale reliably under growing citizen demand. Manual provisioning could not realistically keep pace with that demand.
DPL automated the environment using AWS ECS, Amazon Bedrock, and a GitLab CI/CD pipeline tied directly to infrastructure changes. Every environment change now ships through that same reviewed pipeline.
The results show what disciplined infrastructure automation delivers inside a real public sector constraint. Resolution time dropped 65%, and the platform maintained 99.9% uptime in production. Infrastructure cost also fell 40% alongside the reliability gains achieved.
That kind of consistency is hard to achieve through manual console changes made by different engineers over time. Codifying the infrastructure removed most of that inconsistency almost entirely from day one.
Change history also became far easier to audit once every modification lived in version control. A reviewer can trace exactly who changed what, and why, months after the fact.
Pulumi: Infrastructure as Code with Real Programming Languages
Pulumi takes a developer-first approach to infrastructure as code. Instead of relying on a dedicated configuration language, it lets engineers use familiar programming languages to define, provision, and manage cloud infrastructure.
This makes it particularly appealing to teams that want more flexibility when managing complex infrastructure. Developers can use existing programming skills, libraries, and software development practices rather than learning an entirely new syntax.
What Is Pulumi?
Pulumi is an open-source infrastructure as code platform that allows teams to manage cloud resources using languages such as Python, TypeScript, JavaScript, Go, Java, and C#.
Its workflow revolves around writing infrastructure code, previewing proposed changes, and deploying those changes through the Pulumi CLI or automation workflows.
Unlike traditional declarative configuration tools, Pulumi supports general-purpose programming constructs. Developers can use functions, loops, conditionals, and existing packages to define infrastructure behavior.
Pulumi also maintains a state file to track deployed resources and determine what needs to change during subsequent updates. Its preview-and-update workflow gives teams visibility into infrastructure changes before they reach production.
Why Pulumi Is a Great Option
Pulumi stands out for its programming flexibility, multi-cloud capabilities, and integration with modern development workflows.
Mainly developers praise the following:
- Familiar Programming Languages – Supports Python, TypeScript, JavaScript, Go, Java, and C#. Developers can define infrastructure using languages they already understand, reducing the learning curve associated with specialized configuration languages.
- Programming Flexibility – Supports functions, loops, conditionals, classes, and other programming constructs. This makes it easier to handle complex infrastructure requirements, dynamic configurations, and conditional resource provisioning.
- Multi-Cloud Support – Works with AWS, Azure, GCP, Kubernetes, and other infrastructure providers. Teams can manage resources across different cloud environments using a consistent programming approach.
- Reusable Components – Allows developers to package infrastructure logic into reusable components and share them across projects. This reduces duplicated code and helps standardize infrastructure deployments.
- Testing and Automation – Supports automated infrastructure testing, policy enforcement, and CI/CD integration. Teams can validate infrastructure code before deployment and introduce automated checks into existing development pipelines.
- Stack and State Management – Uses stacks to organize infrastructure into separate environments, such as development, staging, and production. Its state management capabilities track deployed resources and help identify the changes required during updates.
Pulumi is particularly useful for engineering teams that want infrastructure management to feel like an extension of application development. However, its programming flexibility also introduces additional considerations around code complexity, testing, and state management.
AWS CloudFormation: Native Infrastructure Management for AWS
CloudFormation takes a different approach to infrastructure as code. Rather than focusing on programming flexibility or multi-cloud support, it provides a native way to provision and manage AWS infrastructure through reusable templates.
Its biggest advantage is its direct integration with the AWS ecosystem. Teams managing AWS environments can define, deploy, and update infrastructure without relying on external providers or third-party provisioning tools.
What is AWS CloudFormation?
AWS CloudFormation is Amazon’s native infrastructure as code service that allows developers to define cloud resources using declarative JSON or YAML templates.
Instead of manually creating resources through the AWS Management Console, teams describe their desired infrastructure in a template. CloudFormation then interprets those instructions and handles resource provisioning, configuration, dependencies, and updates.
Its basic workflow involves creating a template, deploying it as a stack, and allowing CloudFormation to manage the resources defined within it.
A CloudFormation stack acts as a manageable collection of AWS resources. Teams can update or delete the stack to make corresponding changes to the infrastructure.
CloudFormation also supports change sets, allowing engineers to preview proposed changes before applying them. This provides greater visibility into infrastructure updates and helps reduce the risk of unexpected production disruptions.
Why AWS CloudFormation is a Great Option
CloudFormation’s biggest strengths are its native AWS integration, automated provisioning capabilities, and built-in infrastructure management features.
- Native AWS Integration – Integrates directly with AWS services, allowing teams to provision and manage resources without depending on third-party providers. It supports a wide range of AWS services and keeps infrastructure management within the AWS ecosystem.
- Automated Provisioning – Uses predefined JSON or YAML templates to create and configure infrastructure consistently. This reduces manual setup, minimizes configuration errors, and makes deployments easier to repeat across environments.
- Dependency Management – Automatically identifies relationships between resources and determines the correct order for creating, updating, or deleting them. This is particularly useful when managing interconnected components such as networking, databases, and application services.
- Change Sets – Allows teams to preview proposed infrastructure changes before deployment. Engineers can review which resources will be added, modified, or removed, making infrastructure updates more predictable.
- Rollback Capabilities – Can automatically roll back failed stack operations, helping restore infrastructure to its previous stable state. This reduces the manual effort involved in recovering from unsuccessful deployments.
- Repeatable Deployments – Reusable templates make it easier to replicate infrastructure across AWS accounts, regions, and environments. Teams can maintain consistent configurations without rebuilding resources manually.
- Drift Detection – Identifies differences between deployed AWS resources and their expected template configurations. This helps teams detect manual changes made outside CloudFormation and maintain infrastructure consistency.
CloudFormation is particularly well-suited to organizations that operate primarily or exclusively within AWS. Its native integration simplifies resource management, while features such as change sets, stack management, and drift detection provide useful controls for production environments.
However, its AWS-centric design makes it less suitable for teams seeking a single IaC solution across multiple cloud providers. Organizations managing hybrid or multi-cloud environments may need additional tools to cover infrastructure outside AWS.
Pulumi vs CloudFormation vs Terraform
CloudFormation is AWS-only, but it integrates tightly with nearly every other AWS service by design.
Terraform trades that native depth for breadth across providers instead. A single Terraform codebase can manage AWS, Azure, and GCP resources side by side in one workflow.
Teams fully committed to AWS, with no realistic multi-cloud plans, often find CloudFormation’s native integration worth it. The lock-in rarely bothers them in practice.
Teams expecting any multi-cloud future, even a distant one, tend to value Terraform’s portability instead. The extra setup effort pays off later.
Rollback behavior differs meaningfully between the two tools as well. CloudFormation offers automatic rollback on failure. Terraform generally requires a manual intervention step instead.
Pulumi sits in an interesting middle position between the two. It uses real programming languages like TypeScript and Python, which appeals to teams that want full language tooling.
That familiarity cuts both ways in practice. Pulumi’s learning curve is gentler for engineers already fluent in those languages. It is steeper for infrastructure teams used to declarative syntax instead.
Where IaC Fits in DevOps Automation Services
DevOps automation services treat infrastructure as code as one piece of a larger pipeline. It is not a standalone discipline on its own. IaC alone does not guarantee fast, safe delivery.
Pairing IaC with automated testing catches a bad configuration before it ever reaches a production environment. That testing layer is often the difference between a minor fix and a real outage.
Policy-as-code tooling layered on top of any of these three tools can block risky changes automatically before they ship. That automated check matters more as a team and its infrastructure both grow larger together.
Choosing the right infrastructure as code tools early makes that later automation layer easier to bolt on cleanly. Forcing it in after the fact rarely goes smoothly.
Cloud Migration Tools: Choosing IaC for a Migration, Not Just Greenfield Work
Cloud migration tools and IaC tools overlap heavily. Migration work still adds constraints that greenfield projects simply do not have to deal with. Importing existing, unmanaged infrastructure is its own real challenge.
Terraform’s import functionality lets a team bring existing resources under management gradually. No one has to do it all at once in a single risky pass. That gradual approach reduces risk considerably during a live migration.
Unmanaged resources discovered mid-migration are common, not rare, in most real environments. Budgeting time for that discovery work upfront avoids an unpleasant surprise partway through the project.
The cloud migration services market was valued at $42.0 billion in 2025. It is projected to reach USD 224.7 billion by 2033. That growth reflects how much legacy infrastructure still needs exactly this kind of work.
Most of that legacy infrastructure was never built with any IaC tool in mind. Someone provisioned it manually, years ago, and nobody has touched the process since.
Bringing that infrastructure under management is slow, careful, deliberate work. Rushing it tends to introduce the exact outages a migration effort is supposed to avoid entirely.
Inventorying what already exists is the unglamorous first step most teams are tempted to skip. Doing it before writing any configuration almost always costs less time later, even though it feels slower at first.
Tagging ownership during that inventory pass pays off too, every single time it gets done properly and consistently. Untagged resources become nobody’s responsibility once the original owner moves teams or leaves the company entirely.
Our deeper comparison of Terraform, CloudFormation, and the cloud migration tools that move workloads safely focuses specifically on migration-safe patterns. This guide focuses more broadly on tool selection itself, for both greenfield and migration work alike.
Choosing Infrastructure as Code Tools That Fit Your Stack
Infrastructure as code tools are not interchangeable, despite solving a similar underlying problem on the surface. The right choice depends on cloud strategy, team skills, and existing commitments already in place.
A single-cloud team with deep AWS investment may genuinely prefer CloudFormation’s native
Revisiting that choice periodically keeps the decision from quietly becoming outdated. Teams and their cloud footprints both grow over time.
DPL’s Cloud & DevOps services can further help you make the right choices for your IT infrastructure. Let us know how we can help in the form below.

Topics
Related Articles
-
Disaster Recovery Companies – What to Evaluate Beyond SLA Guarantees
04-Nov-2026 Maha Yaser
-
Hiring App Modernization Services to Effectively Break Monoliths into Microservices
23-Sep-2026 Hazar Hayat
-
How Kubernetes Orchestration Works at Scale — and Why It Matters for Container Management
22-Sep-2026 Hazar Hayat